The table of content
InfinitySDLC Engineering Guides · 09/12
Reference implementation guide, not a report of a completed client deployment. Code, configurations, metrics and policies are illustrative. Adapt and validate them before production use.
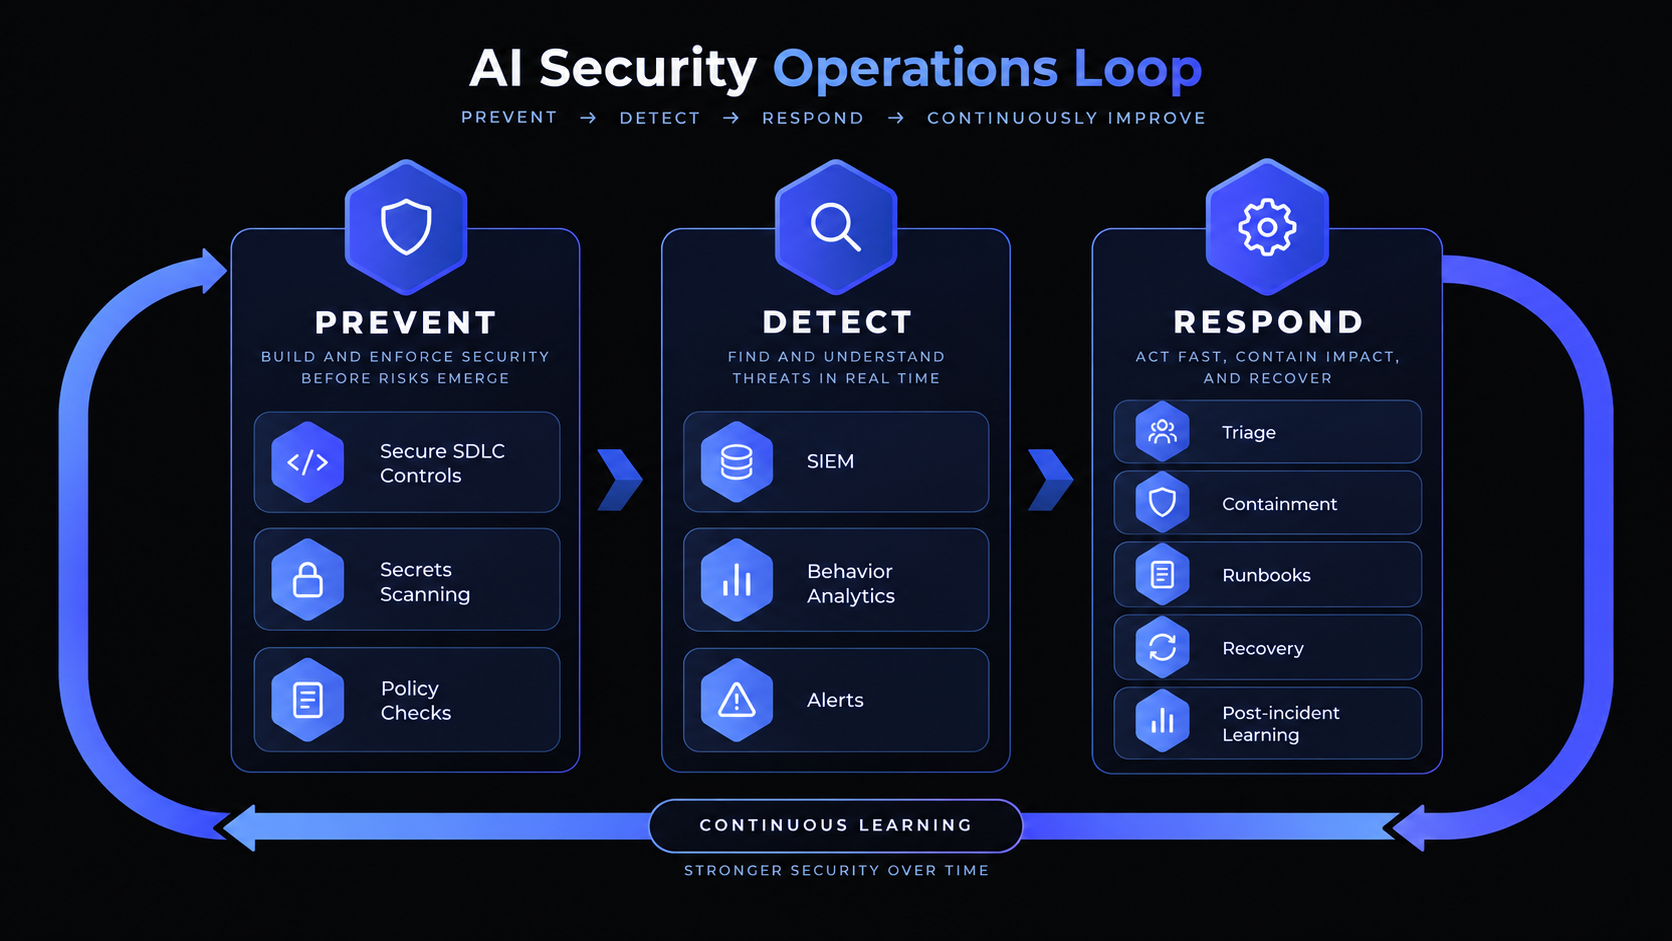
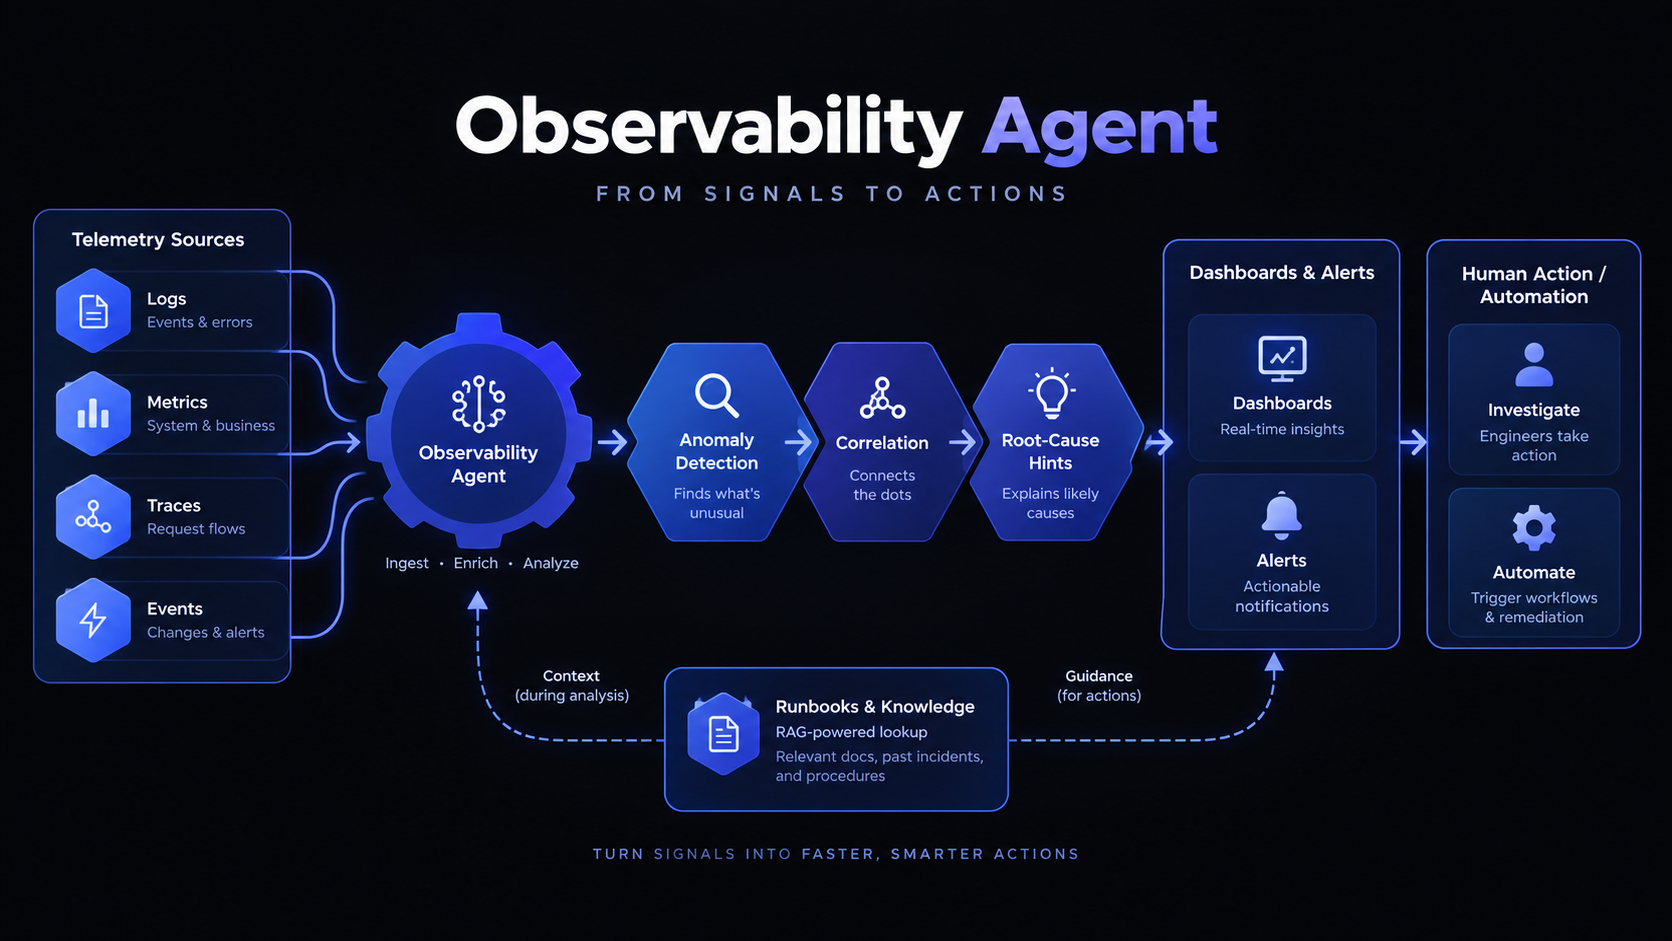
The Threat Detection Agent is a bounded analyst that enriches and correlates detections. It should increase signal quality and investigation speed without giving a language model unrestricted powers to disable users, block networks or delete workloads.
9.1 Inputs
- SIEM alerts and normalized event schemas.
- EDR findings and process trees.
- Cloud audit logs and IAM events.
- Identity provider sign-in/risk events.
- Network/DNS/proxy telemetry.
- Asset inventory, vulnerability state and ownership.
- Recent deployments/config changes from the release system.
- Threat intel feeds accessed through curated tools.
9.2 Detection triage workflow
- Parse alert into entities: actor, host/workload, IP/domain, process, cloud resource, time.
- Enrich each entity using bounded tools.
- Build a timeline from normalized events, preserving source and timestamp.
- Compare against known-good deployment/change events to reduce benign positives.
- Map behavior to internal detection taxonomy/MITRE-style techniques if used by the organization.
- Produce disposition options with confidence and missing evidence.
- For containment, create a proposed action set and require SOC approval except for pre-authorized low-risk automation.
triage:
  alert_id: SIEM-99182
  entities: [user:u1042, host:wks-044, domain:example.invalid]
  disposition: suspicious
  confidence: 0.86
  evidence:
    - edr_process_tree: ...
    - idp_signin: impossible_travel=false
    - dns_first_seen: 12m
  recommended_next:
    - collect_edr_package
    - revoke_session   # approval required
  destructive_actions: none_executed
9.3 Retrieval strategy
RAG should hold detection runbooks, asset criticality, approved admin tooling, past incident patterns and exception knowledge. Threat telemetry itself should be queried from the SIEM/data lake with strict time/entity filters. Use a local model for high-volume alert summarization if regulatory or security policy prohibits external inference.
9.4 Evaluation on replay datasets
- Replay known incidents and benign operational events.
- Measure false-positive reduction and true-positive preservation.
- Score timeline correctness and entity-resolution accuracy.
- Test against poisoned log fields and adversarial ticket text.
- Track whether the agent requested dangerous containment actions without sufficient evidence.
Implementation Blueprint: Correlation Without Unbounded Containment
Build deterministic entity resolution
Canonicalize users, cloud principals, hosts, containers, IPs and applications outside the model. Correlation quality collapses when the agent must infer whether four aliases represent the same principal.
canonical_entity: principal:8d21
aliases:
  - idp:user:alice@example.com
  - aws:...:role/ops-admin
  - github:user:alice
risk_context:
  privileged: true
  owner_team: platform
  last_role_change: 2026-09-02
Containment policy
| Action | Default |
|---|---|
| Collect forensic package | automatic in alert scope |
| Increase telemetry/snapshot | automatic within quota |
| Block domain/IP | approval unless exact IOC is preapproved |
| Revoke session | SOC approval |
| Disable user / isolate host | SOC approval; stronger for privileged identities |
| Delete resource | not exposed as an agent containment primitive |
Containment is a proposal produced by the agent and an action executed by a separately authenticated enforcement service. This prevents malicious SIEM content from directly turning into firewall or identity actions.
Source and Shared Prerequisites
Adapted from the September 2026 Enterprise AI Agent Mesh handbook, Article 9 and Blueprint 9. The Enterprise Agent Platform Foundation guide provides the shared identity, MCP, retrieval, sandbox, audit and evaluation design, plus the source handbook’s further-reading list. Validate model, protocol and tool versions before production use.
Explore the Series


Our success stories











Tell us about your project needs